AI-driven runtime bug and vulnerability hunter that runs your app in a production-like sandbox
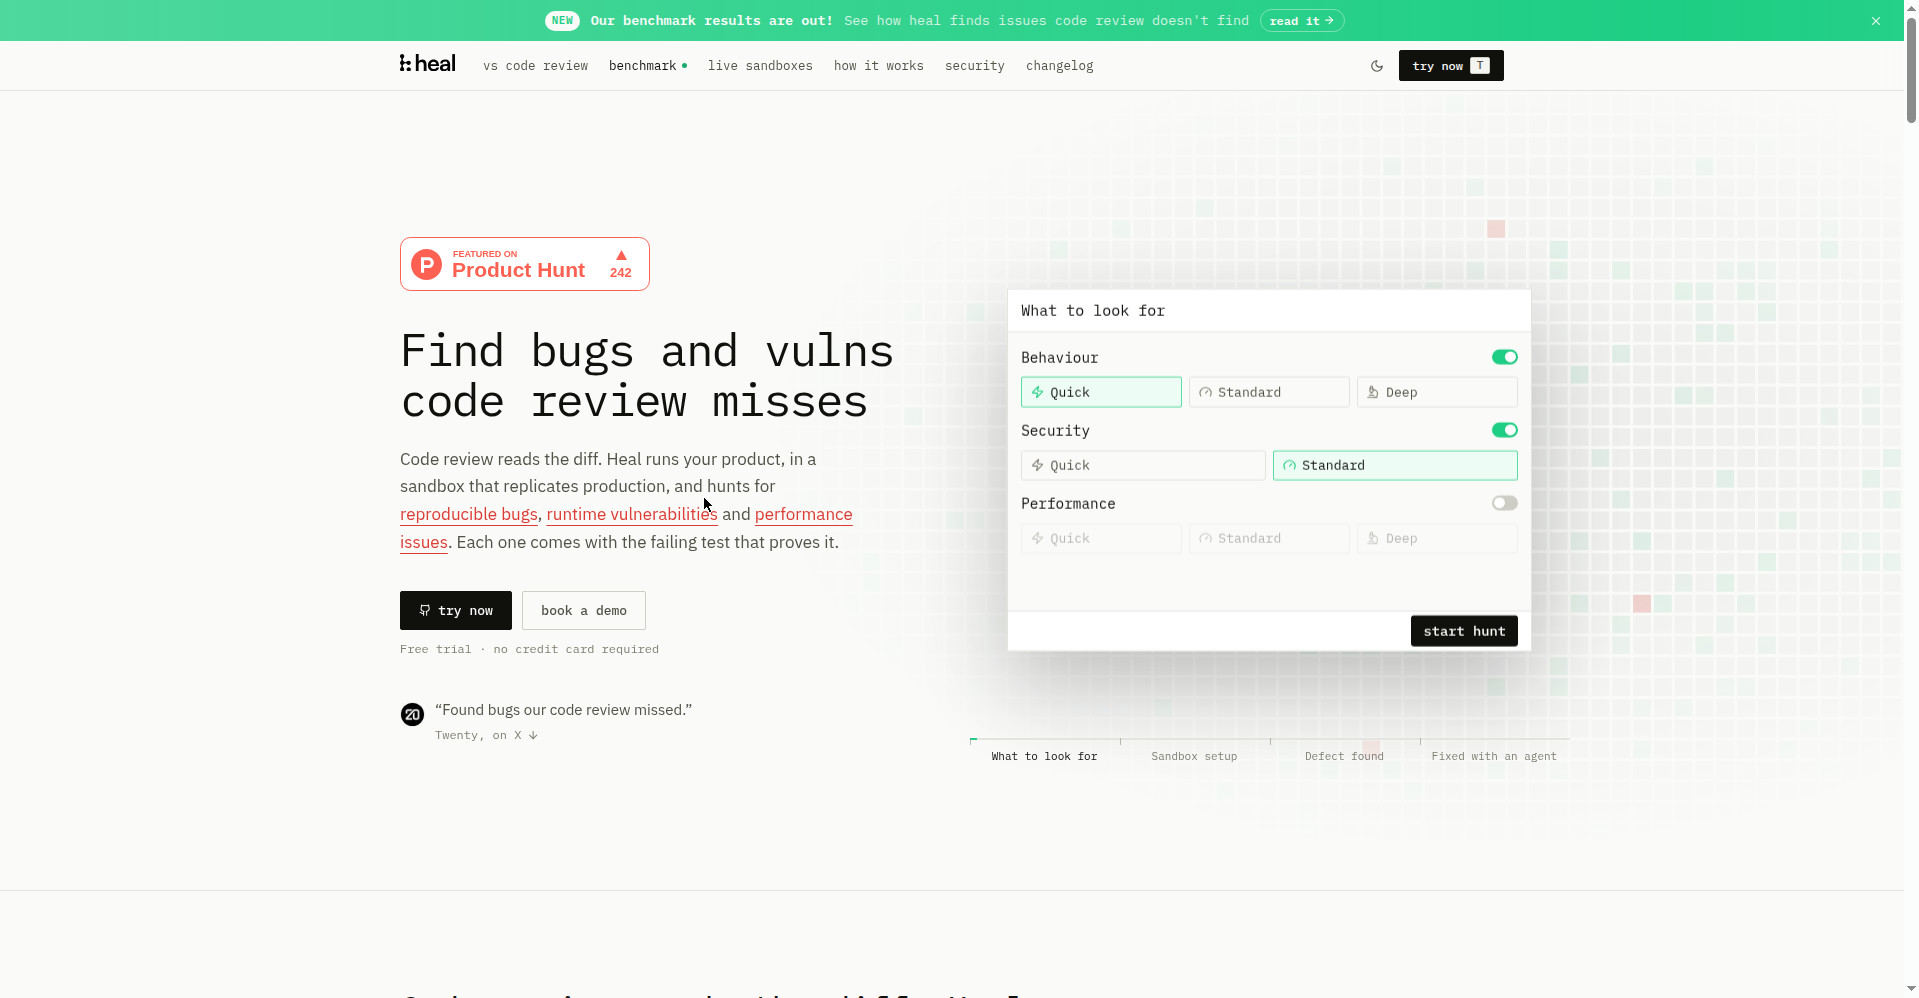
Homepage
1 / 2Overview
What is heal.dev?
Find bugs and vulnerabilities code review misses
heal.dev is an AI-driven bug and vulnerability detection service built for teams that rely on AI coding assistants. Instead of reading code diffs like a traditional reviewer, heal.dev learns to run your application in a production-like sandbox that replicates your live environment and stubs external services.
Once running, it hunts for reproducible bugs, runtime vulnerabilities and performance issues - the problems code review typically misses. It validates findings with real attack simulations, so only issues it can actually reproduce are reported. Every defect arrives with reproduction steps, a screenshot and a failing test that proves the problem exists.
heal.dev also integrates with popular security scanners such as ZAP, nuclei, semgrep, trufflehog, sqlmap, schemathesis, dalfox and jwt_tool, and exposes an API and MCP server so coding agents can work with it directly.
Pricing is freemium: there is a free trial with no credit card required, it is free for open source projects, and enterprise customers can opt for a single-tenant deployment. The service is SOC 2 Type 2 certified, with AES-256 encryption at rest and TLS 1.2+ in transit.
Platforms and languages
heal.dev Availability
Platforms
Languages
Capabilities
heal.dev Key Features
Production-like sandbox
Learns to run your app in a sandbox that replicates production, stubbing external services.
Runtime bug hunting
Actively hunts for edge cases, performance problems and vulnerabilities while your app runs.
Real attack validation
Validates findings with simulated attacks using two identities, so only truly reproducible issues are reported.
Actionable defect reports
Every defect ships with reproduction steps, a screenshot and a failing test that proves it.
Scanner integrations
Integrates popular scanners including ZAP, nuclei, semgrep, trufflehog, sqlmap, schemathesis, dalfox and jwt_tool.
Best for
Who uses heal.dev?
Dev teams using AI coding assistants
Catch runtime bugs, vulnerabilities and performance issues that code review misses
Plans and access
heal.dev Pricing
Freemium
Free trial with no credit card required; free for open source; enterprise single-tenant plans available.
Common questions
heal.dev FAQs
Is there a free trial?
Yes. You can start with a free trial without a credit card, and heal.dev is also free for open source projects. Enterprise single-tenant deployments are available for larger organizations.
How is heal.dev different from a code review tool?
Code review reads the diff. heal.dev actually runs your product in a sandbox that replicates production and hunts for reproducible bugs, runtime vulnerabilities and performance issues. Each finding comes with reproduction steps, a screenshot and a failing test that proves it.
How does heal.dev handle security and my data?
heal.dev is SOC 2 Type 2 certified, encrypts data with AES-256 at rest and TLS 1.2+ in transit, and isolates tenants at the row level. Enterprise customers can run a single-tenant deployment, and permanent data deletion is supported.
Does heal.dev run a bug bounty program?
No paid bug bounty program. You can report vulnerabilities to [email protected]; reports are acknowledged within 24 hours and triaged within 72 hours.
Reviews
See what the community thinks and share your experience.
—
Based on 0 ratings
Rating distribution
Community reviews
No reviews
No written reviews yet.