Rizzqo
Asset-first compliance execution for ISO 27001, NIS2, DORA and the EU AI Act. Every requirement lands on a real asset, with a named owner and evidence attached. Made in Germany.
Asset-first compliance execution for ISO 27001, NIS2, DORA and the EU AI Act. Every requirement lands on a real asset, with a named owner and evidence attached.
screen1.jpeg
Overview
What is Rizzqo?
Asset-first compliance execution for ISO 27001, NIS2, DORA and the EU AI Act. Every requirement lands on a real asset, with a named owner and evidence attached. Made in Germany.
Rizzqo is asset-first compliance execution software for regulated organizations, made in Germany and hosted in the customer's own country.
Most compliance tools start with a framework and end with a checklist. They tell you what a standard requires, but never which server, database or SaaS tool has to be configured and who is responsible. Rizzqo starts from the organization instead. You model your critical services, information and processes, the applications, systems, infrastructure and suppliers they depend on, and who owns each. Controls from ISO 27001, ISO 27002, NIS2, DORA, GDPR, EU AI Act, TISAX and NIST CSF 2.0 are translated into requirements per asset type and applied automatically to every matching asset. The owner answers, attaches evidence and confirms with a logged timestamp. Compliance status is calculated from confirmed answers, never self-declared. One requirement can satisfy controls from several frameworks, so work is done once.
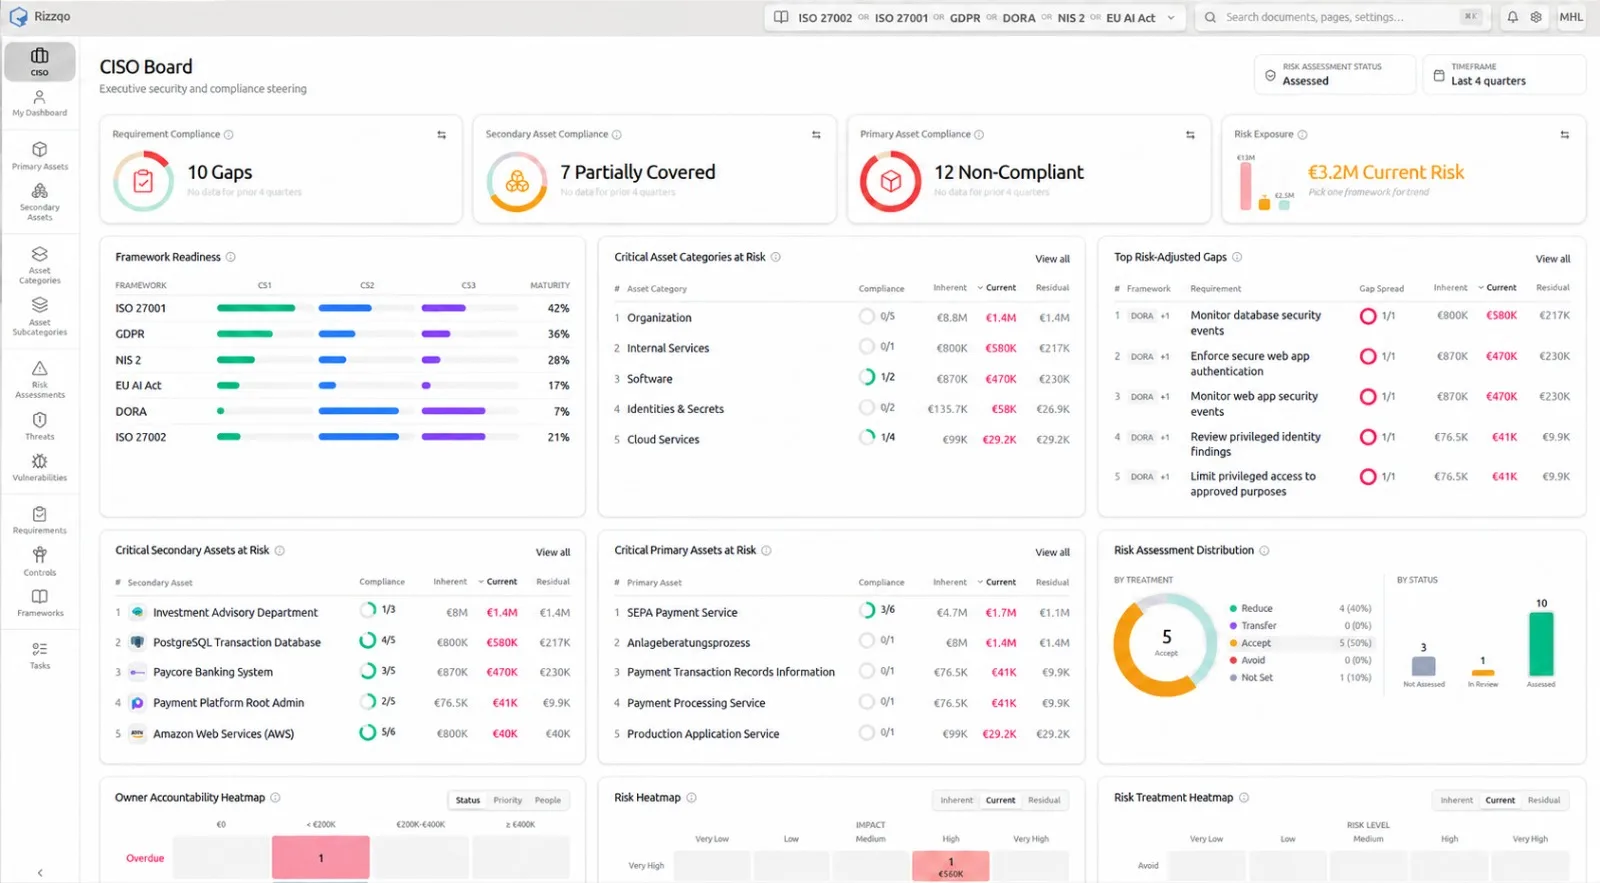
Open requirements are visible as gaps. Gaps become risk assessments with inherent, current and residual scoring, a monetary value and a documented treatment decision. Remediation tasks are assigned, tracked and synchronized with Jira. Dashboards show ISMS teams and CISOs framework readiness and which critical business services are exposed by unfinished work. Suppliers, personal data flows and AI systems are handled in the same asset model.
Rizzqo is built for ISMS managers, information security managers and CISOs in regulated mid-sized organizations across Europe. It can run on-premises or in a cloud in the customer's country, with SSO and SCIM, audit log and daily backups. Annual subscription per organization, pricing on request.
Platforms and languages
Rizzqo Availability
Platforms
Languages
Capabilities
Rizzqo Key Features
Rizzqo
Asset-first compliance execution for ISO 27001, NIS2, DORA and the EU AI Act. Every requirement lands on a real asset, with a named owner and evidence attached. Made in Germany.
Plans and access
Rizzqo Pricing
Paid
0
Rizzqo is asset-first compliance execution software for regulated organizations, made in Germany and hosted in the customer's own country.
Most compliance tools start with a framework and end with a checklist. They tell you what a standard requires, but never which server, database or SaaS tool has to be configured and who is responsible. Rizzqo starts from the organization instead. You model your critical services, information and processes, the applications, systems, infrastructure and suppliers they depend on, and who owns each. Controls from ISO 27001, ISO 27002, NIS2, DORA, GDPR, EU AI Act, TISAX and NIST CSF 2.0 are translated into requirements per asset type and applied automatically to every matching asset. The owner answers, attaches evidence and confirms with a logged timestamp. Compliance status is calculated from confirmed answers, never self-declared. One requirement can satisfy controls from several frameworks, so work is done once.
Open requirements are visible as gaps. Gaps become risk assessments with inherent, current and residual scoring, a monetary value and a documented treatment decision. Remediation tasks are assigned, tracked and synchronized with Jira. Dashboards show ISMS teams and CISOs framework readiness and which critical business services are exposed by unfinished work. Suppliers, personal data flows and AI systems are handled in the same asset model.
Rizzqo is built for ISMS managers, information security managers and CISOs in regulated mid-sized organizations across Europe. It can run on-premises or in a cloud in the customer's country, with SSO and SCIM, audit log and daily backups. Annual subscription per organization, pricing on request.
Compare similar tools
Rizzqo Alternatives
Reviews
See what the community thinks and share your experience.
—
Based on 0 ratings
Rating distribution
Community reviews
No reviews
No written reviews yet.