AI on-call engineer that investigates production incidents inside your network, proves the root cause, and applies fixes with your approval.
How 3AM works
1 / 2Overview
What is 3AM Super Intelligence?
Sleep through the 3am page.
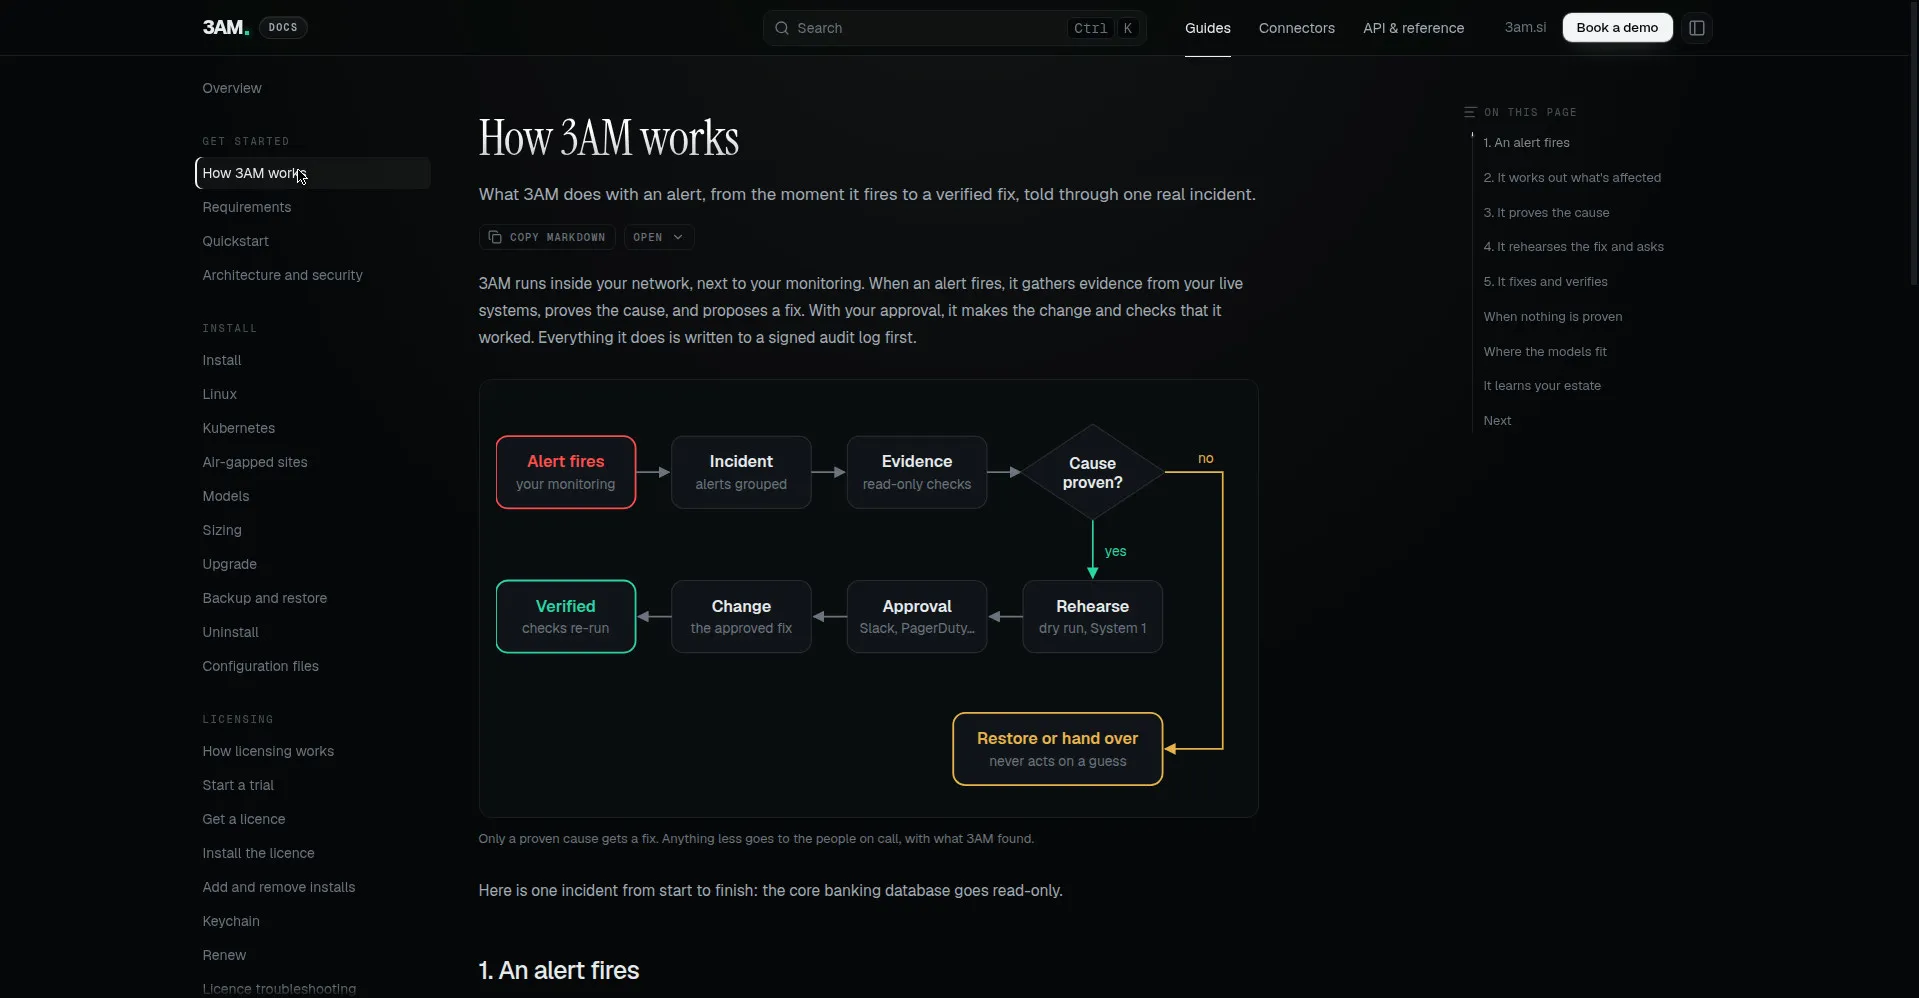
3AM is the AI on-call engineer for systems you can't rewrite. When a production alert fires, 3AM gathers evidence from your live systems, proves the root cause, rehearses the fix, and resolves the incident with one tap of approval in Slack — all from inside your network. It starts in shadow mode, acts only with human approval, and writes every action to a tamper-evident audit ledger. Built for regulated enterprises (banks, insurers, telcos, public sector) with on-prem and air-gapped deployment. Licensed software with a free trial; book a demo for pricing.
Platforms and languages
3AM Super Intelligence Availability
Platforms
Languages
Capabilities
3AM Super Intelligence Key Features
Root-cause proof
Gathers evidence from your live systems and proves the cause with read-only checks before proposing any fix.
Fix rehearsal
Dry-runs every fix before applying it, so only verified changes ever reach production.
Human-approved actions
Resolves incidents with one tap in Slack; starts in shadow mode and changes nothing until you allow it.
Runs inside your network
On-prem install with no inbound ports; open-weight models run locally on GPU, and air-gapped deployments are supported.
Tamper-evident audit trail
Every action is written to a signed, hash-chained ledger that exports to your SIEM for auditors.
Best for
Who uses 3AM Super Intelligence?
On-call engineers and SRE teams at regulated enterprises
Resolve production incidents on systems that cannot be rewritten, with proof and approval
Plans and access
3AM Super Intelligence Pricing
Paid
Licensed software with free trial (90-day launch offer); book a demo for pricing.
Common questions
3AM Super Intelligence FAQs
Can 3AM change production without a person approving it?
Not unless you allow it. Every service starts in shadow mode where 3AM only proposes; L1 actions need one approval, and a global halt stops everything at once.
What stops it acting on the wrong root cause?
Only a cause confirmed by read-only checks against your live systems can lead to a fix. Runbooks can suggest causes but never authorize action, and every fix is dry-run first.
Which AI models does it use?
Open-weight models that run inside your install on GPU — nothing calls out to external services.
How do auditors verify what happened?
Every event goes into an append-only, hash-chained ledger with signed segments; an independent verifier detects tampering and the ledger exports to your SIEM.
Can it run in an air-gapped environment?
Yes. The air-gap bundle ships container images and model weights together, so nothing needs fetching at install time.
Reviews
See what the community thinks and share your experience.
—
Based on 0 ratings
Rating distribution
Community reviews
No reviews
No written reviews yet.